Raw text to clean fields.
Watch live syslog, select sample messages, and build named-capture regex rules. Ask AI to help generate an extraction, then test it before saving.
Live streamJSON previewAI model selection
Turn noisy syslog into structured, enriched JSON. Build extraction rules with AI, investigate threat-intel matches, and send clean events to OpenSearch—from one workbench.
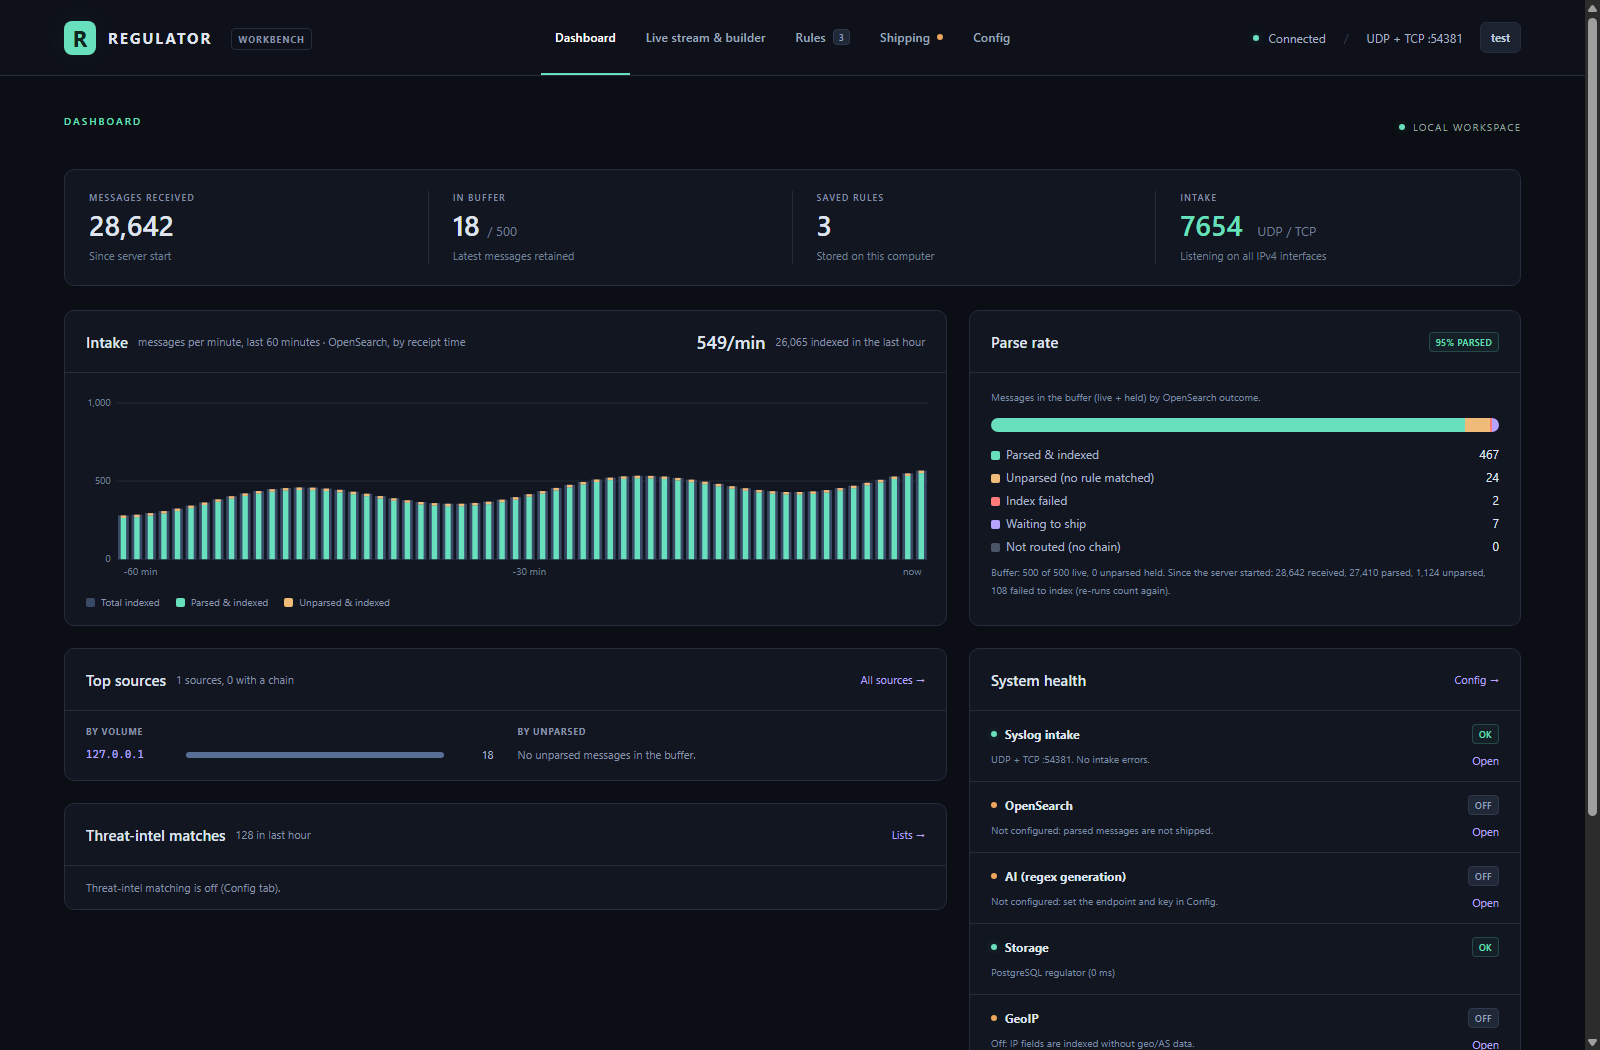
No more guessing what a field means or whether an event made it through. Keep parsing, enrichment, and routing in view.
Watch live syslog, select sample messages, and build named-capture regex rules. Ask AI to help generate an extraction, then test it before saving.
Add optional GeoIP, domain, URL, user-agent and network context. Choose individual FireHOL lists or configure custom indicator feeds.
Organize sources into groups, apply ordered rule chains, and route structured events to dataset-based OpenSearch data streams.
Give event managers the tools to work with logs and rules, while system administrators manage configuration and users. Run collector, processor and UI roles separately.
Actual Regulator screens, populated with illustrative demo data. Click any screenshot for a closer look.
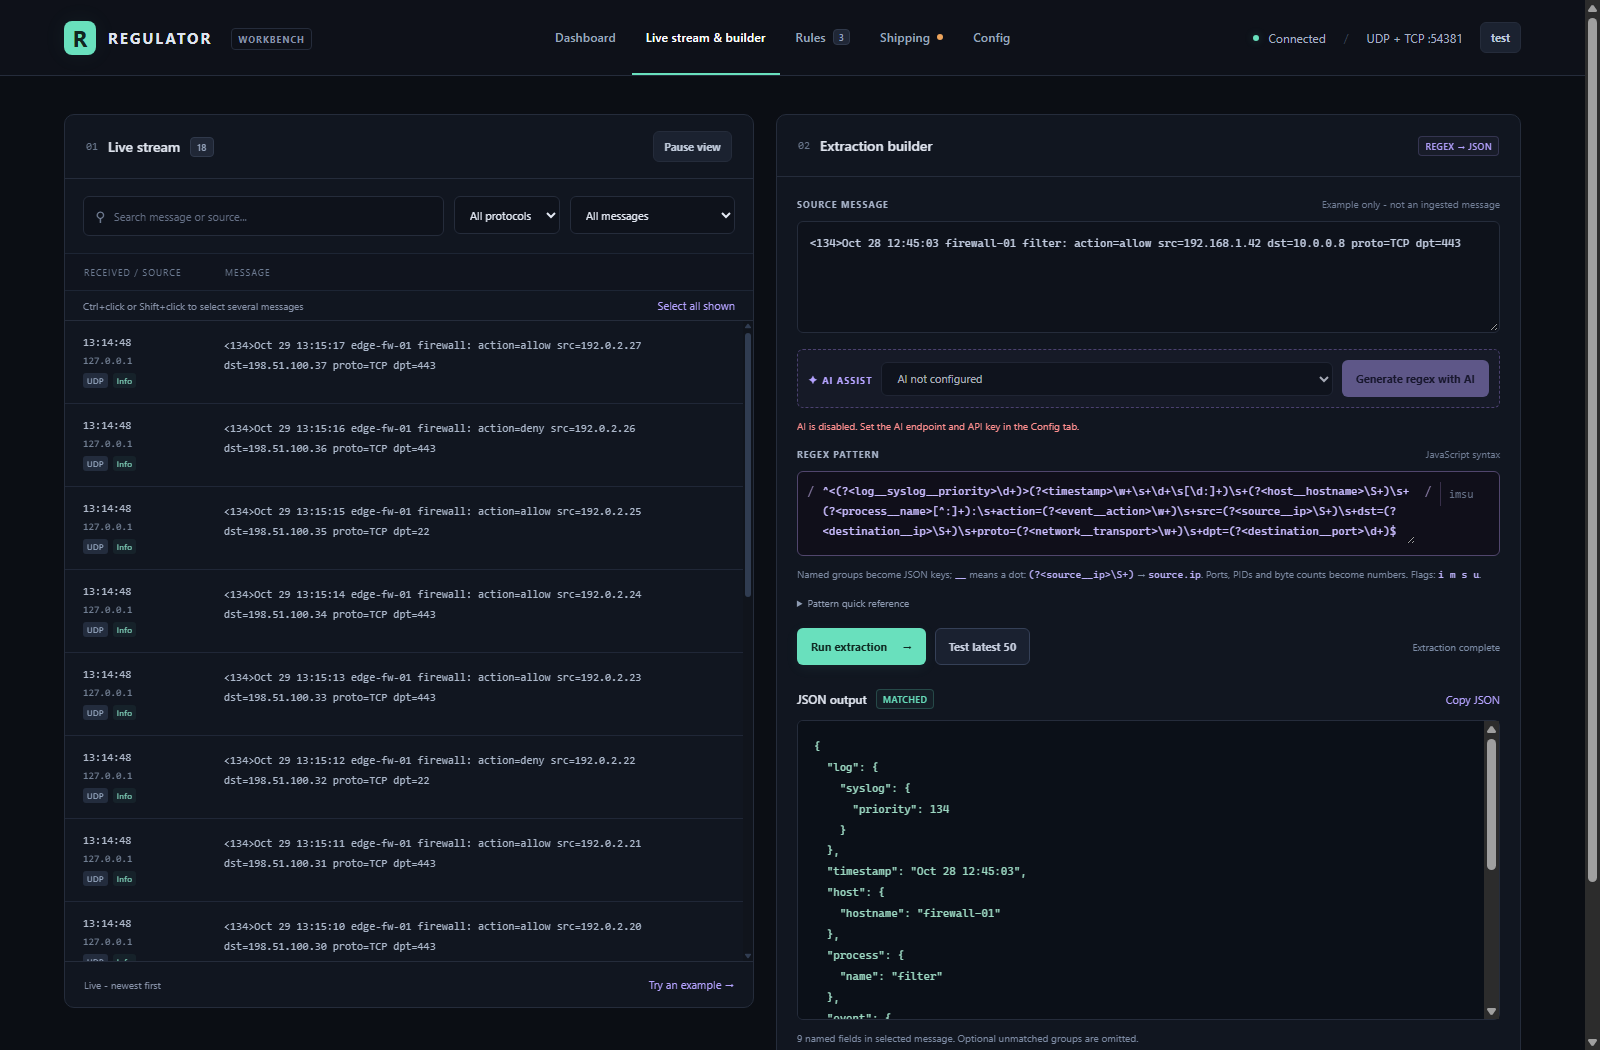
Work directly with log samples, extraction rules, and JSON results.
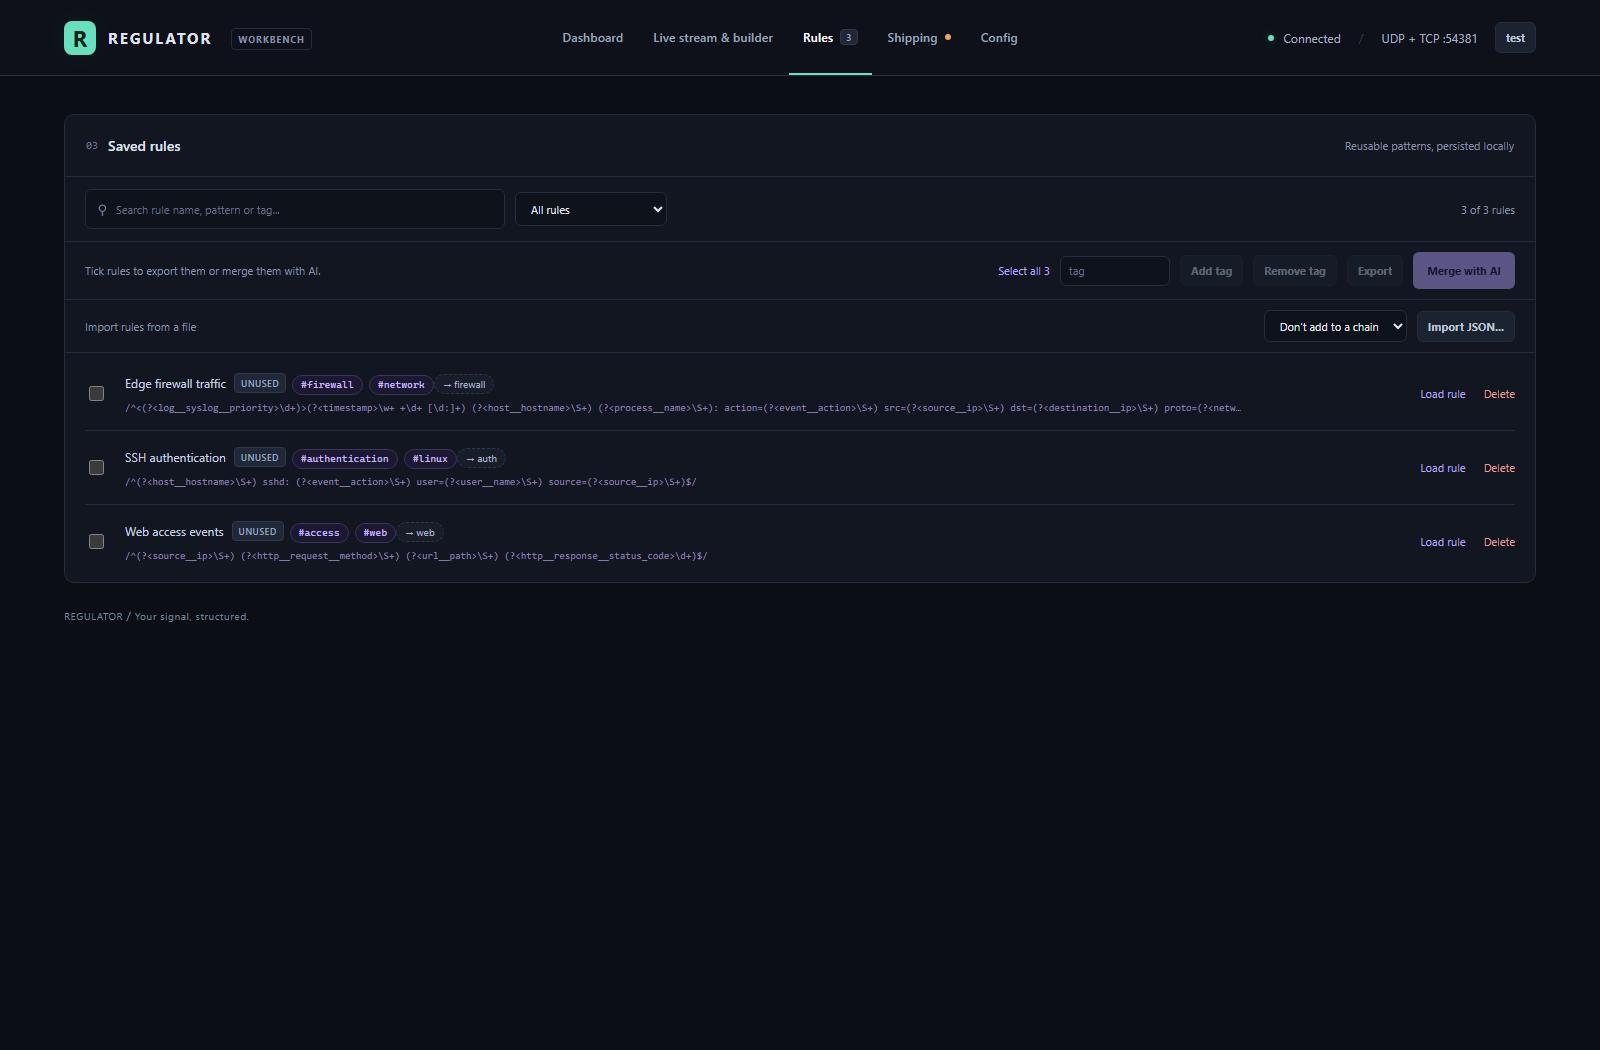
Keep rules organized, tagged, and ready to apply to your sources.
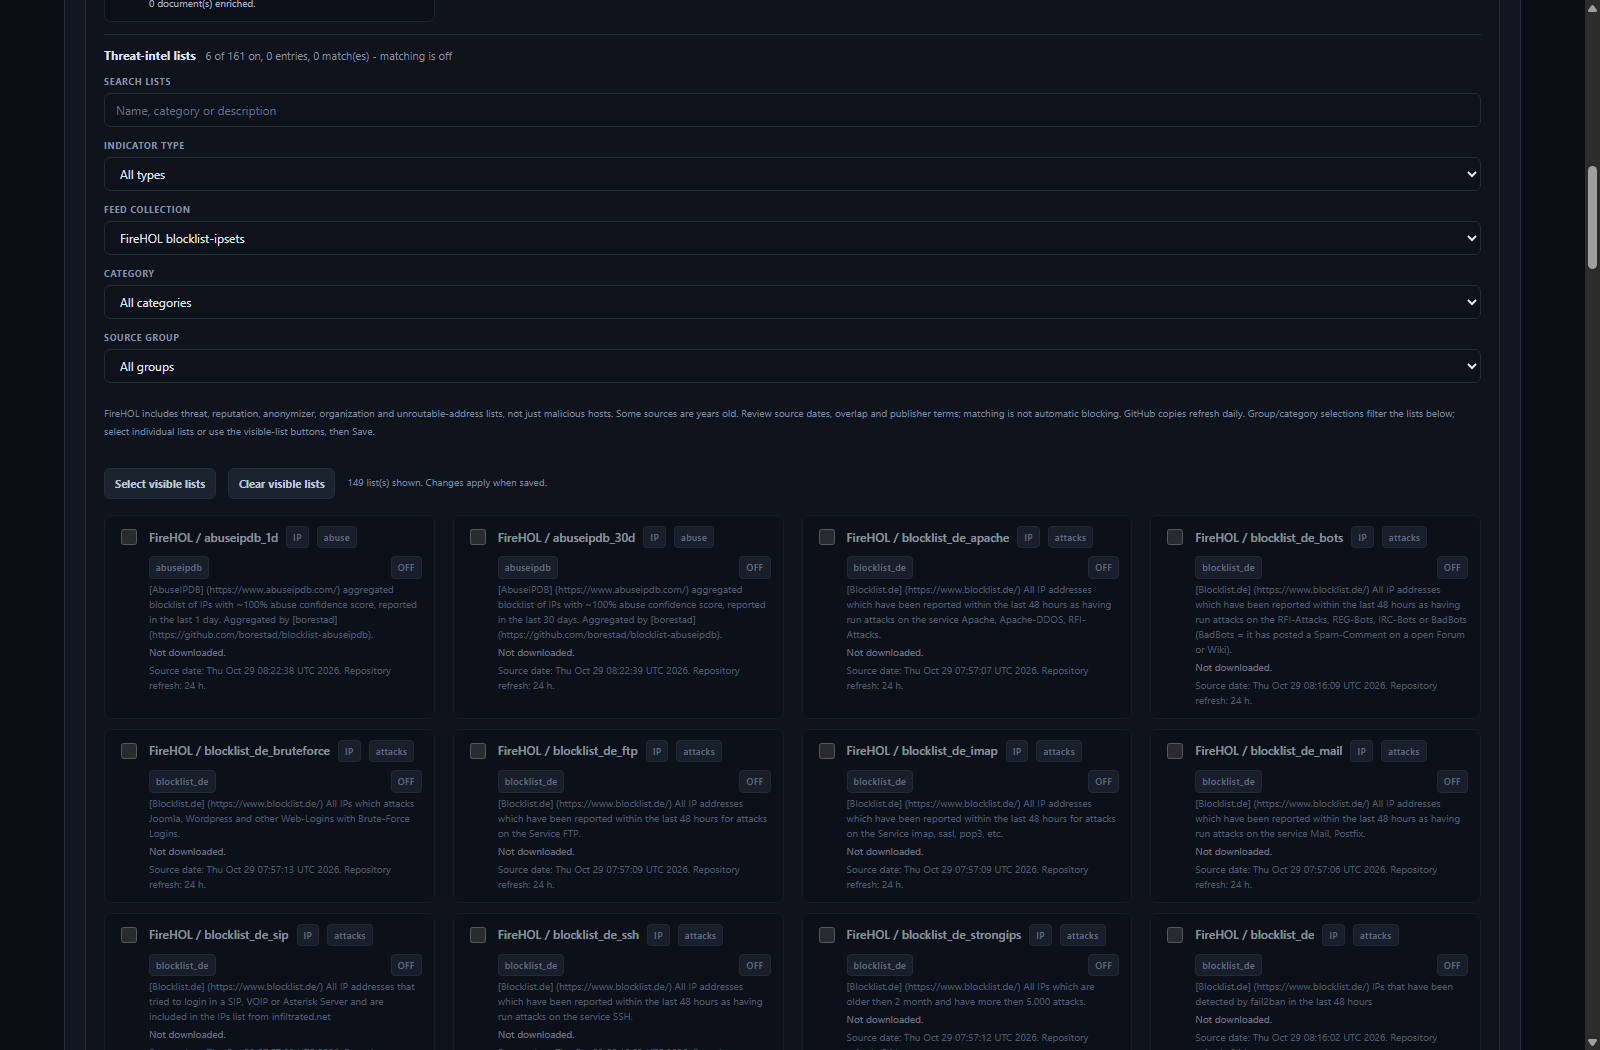
Select the feeds that matter to your environment. Matches add context, not a verdict.
Want a closer look at Regulator? Get in touch to discuss your logging workflow or arrange a walkthrough.
Contact us art@artlebel.com